
From Compliance Requirements to Cyber Resilience
Executive cybersecurity leadership helping organisations achieve NIS2, DORA and ISO 27001 compliance while reducing cyber risk, strengthening governance and improving operational resilience.
Your Trusted Partner on the Journey to Compliance
Gain strategic leadership, risk management expertise and practical support to meet the requirements of NIS2, DORA and ISO 27001.
🔹 NIS2
Achieve readiness for the latest European cybersecurity requirements.
🔹 DORA
Strengthen operational resilience and improve risk management capabilities.
🔹 ISO 27001
Build and maintain an effective Information Security Management System.
🔹 Virtual CISO
Executive leadership, governance oversight and long-term cyber resilience.
30-minute expert consultation • No obligation
Why Organisations Turn to a Virtual CISO
Today's organisations face increasing cyber threats, growing regulatory pressure, customer expectations and board-level accountability. Yet many lack the leadership, governance and expertise needed to manage cyber risk effectively.
⚠️ Limited Risk Visibility
Leadership lacks a clear understanding of the organisation's cyber risks, their business impact and the current level of exposure.
⚠️ Lack of Cybersecurity Leadership
The organisation has no dedicated CISO or relies solely on technical teams without strategic cyber risk oversight.
⚠️ Growing Regulatory Pressure
NIS2, DORA, ISO 27001, GDPR and other frameworks require demonstrable governance, accountability and risk management.
⚠️ Customer & Partner Expectations
Customers increasingly expect evidence of cybersecurity maturity, resilience and security governance.
⚠️ Difficult Decision-Making
Complex cybersecurity topics are often difficult to translate into business language and actionable decisions.
⚠️ Preparing for Growth
New clients, markets and partnerships require stronger cybersecurity, governance and risk management capabilities.
Our role is to help leadership understand risk, make informed decisions and build a resilient organisation capable of navigating both cyber threats and an increasingly complex regulatory landscape.
What Is the Cost of Poorly Managed Cyber Risk?
Cyber incidents are rarely just technical problems. They impact revenue, customer confidence, operations and business reputation.
📉 Financial Losses
Business disruption, lost revenue, emergency response costs and recovery expenses.
🤝 Loss of Trust
Customers, partners and investors may lose confidence in the organisation.
📋 Regulatory Consequences
Investigations, penalties, corrective actions and increased oversight.
⛔ Operational Disruption
Inability to deliver services, production stoppages or delays to critical operations.
⚖️ Increased Executive Accountability
Boards and executives are increasingly held accountable for risk management.
📈 Limited Growth Opportunities
Weak security governance can delay new customers, markets and strategic partnerships.
Organisations that manage risk proactively are better prepared for growth, more resilient during incidents and more successful in meeting regulatory expectations.
How Does a Virtual CISO Turn Risk into Control?
A Virtual CISO provides the governance framework, leadership and expertise needed to help organisations make informed cybersecurity decisions with confidence.
📊 Risk Visibility
Identify critical risks, understand business impact and prioritise mitigation activities.
🏛 Executive Support
Translate complex cybersecurity topics into actionable business decisions.
⚖️ Compliance Management
Navigate NIS2, DORA, ISO 27001, GDPR and other regulatory requirements with confidence.
🛡 Security Improvement
Build policies, controls, governance processes and cyber resilience capabilities.
📋 Audit Readiness
Maintain documentation, evidence and readiness for customer and regulatory audits.
🚀 Long-Term Resilience
Continuously strengthen security capabilities as the organisation grows and evolves.
It provides executive leadership, strategic oversight and independent expertise that help organisations manage cyber risk more effectively and make better-informed decisions.
What Do Organisations Achieve?
Effective cyber risk management is about more than compliance. It creates confidence, resilience and stronger foundations for business growth.
Better Executive Decision-Making
Leadership gains a clearer understanding of risks, priorities and business impact.
Reduced Business Risk
Lower likelihood of incidents, operational disruption and unexpected financial losses.
Increased Trust
Customers, partners and stakeholders gain confidence in the organisation’s governance and security posture.
Audit Readiness
Well-organised processes, documentation and evidence supporting regulatory and customer requirements.
Support for Growth
Security becomes a business enabler when pursuing new markets, opportunities and strategic partnerships.
Long-Term Resilience
Build a sustainable foundation for future business, security and regulatory challenges.
The real value lies in helping organisations make informed decisions, manage risk effectively and grow with confidence in an increasingly complex digital environment.
Expertise Built on Practice, Not Theory
We combine executive leadership, hands-on experience, cloud expertise, modern technologies and delivery of complex projects to help organisations manage risk and build secure, resilient digital environments.
15+ Years of Direct Cybersecurity Experience
Practical expertise in cybersecurity, risk management and the protection of critical business operations.
International Project Experience
Participation in projects across multiple countries, industries and regulatory environments.
Enterprise CTO / CISO Leadership
Executive-level experience that helps translate complex technology and cybersecurity topics into clear business decisions.
Public Cloud & Cloud Security Expertise
A rare combination of cloud architecture, cloud security and governance expertise at enterprise scale.
Multi‑Vendor Technology Ecosystem
Practical expertise across Cloud Security, Endpoint Protection, EDR/XDR/MDR, SIEM/SOAR, Vulnerability Management, Backup & Recovery and Identity Security solutions.
Software Development & System Integration
Our software development practice provides hands-on experience in SaaS delivery, system integration and implementation of complex digital platforms.
CISOEdu.com
Bulgaria's first modern cybersecurity awareness platform designed to reduce human risk and promote a security-first culture.
CISOLead.com
A self-assessment platform helping organisations evaluate their NIS2 readiness and identify critical improvement areas.
SECAAS2B.com
A practical platform showcasing essential cybersecurity, resilience and risk management solutions required by modern organisations.
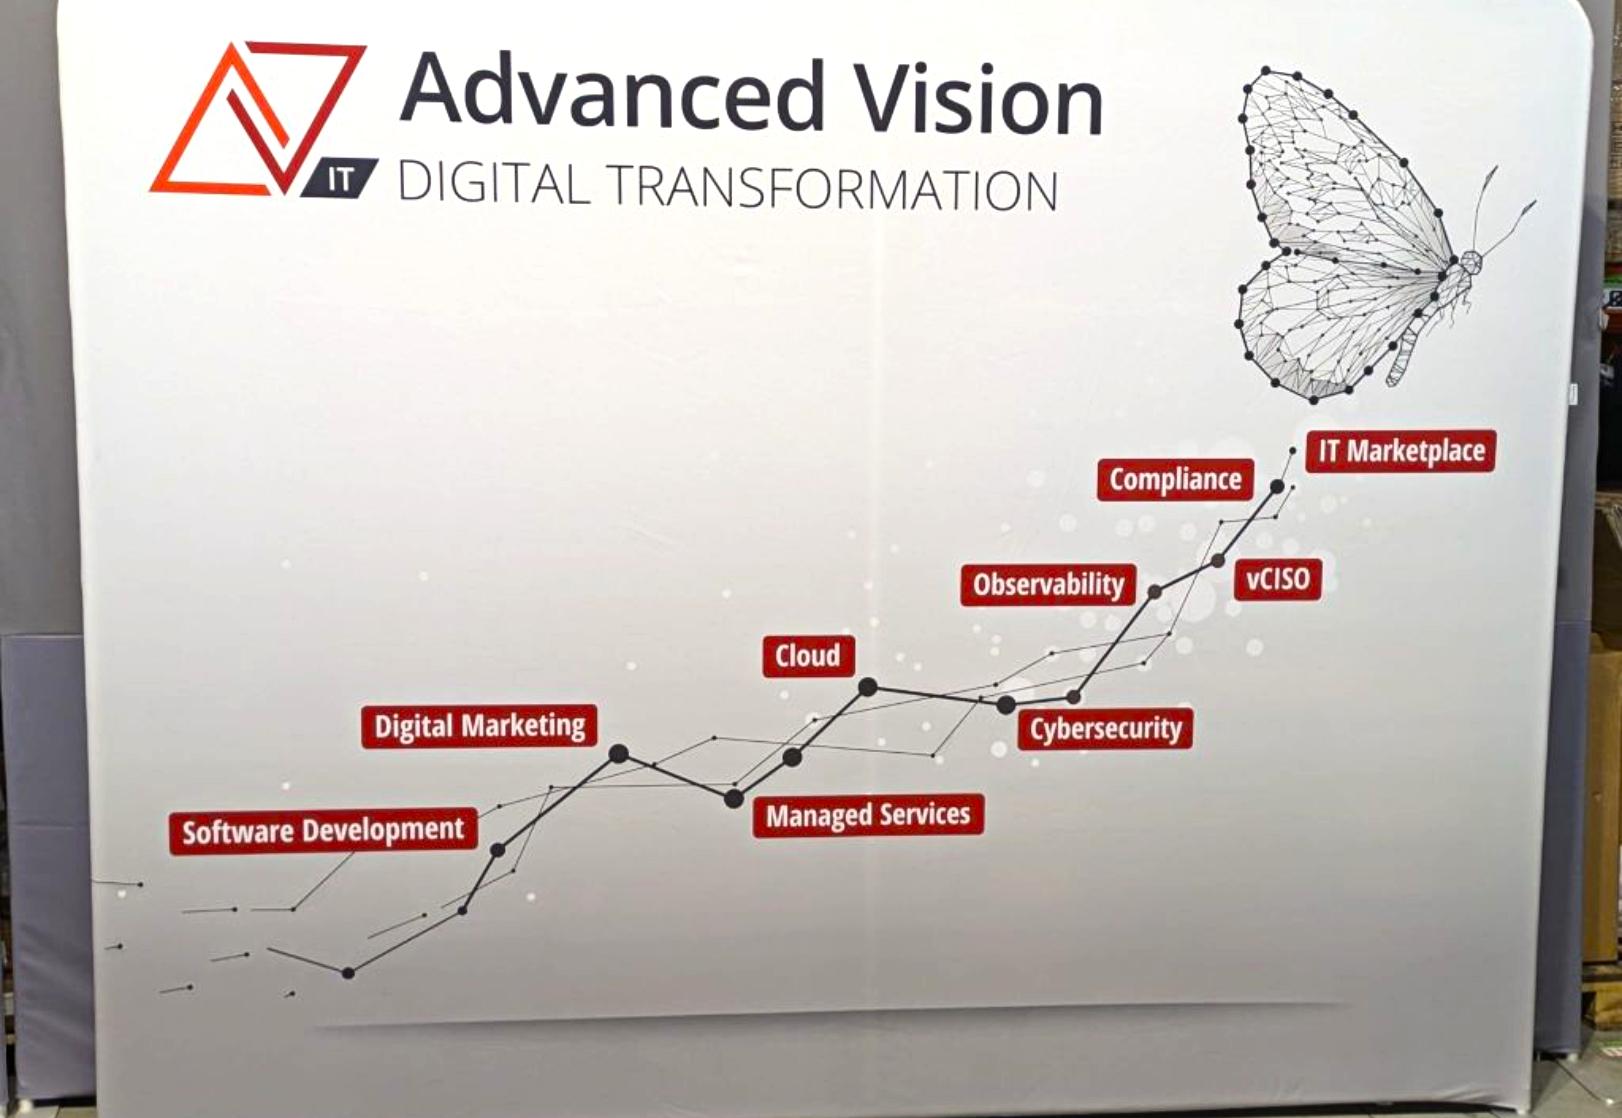
Areas of Expertise
Technologies & Platforms
We operate at the intersection of business, risk, cloud technologies, software engineering, security management and regulatory compliance. This enables us to help organisations build secure, resilient and successful digital businesses.
We actively share expertise and best practices through technical podcasts, cybersecurity awareness initiatives and collaboration with leading global technology vendors.
Expertise in Action
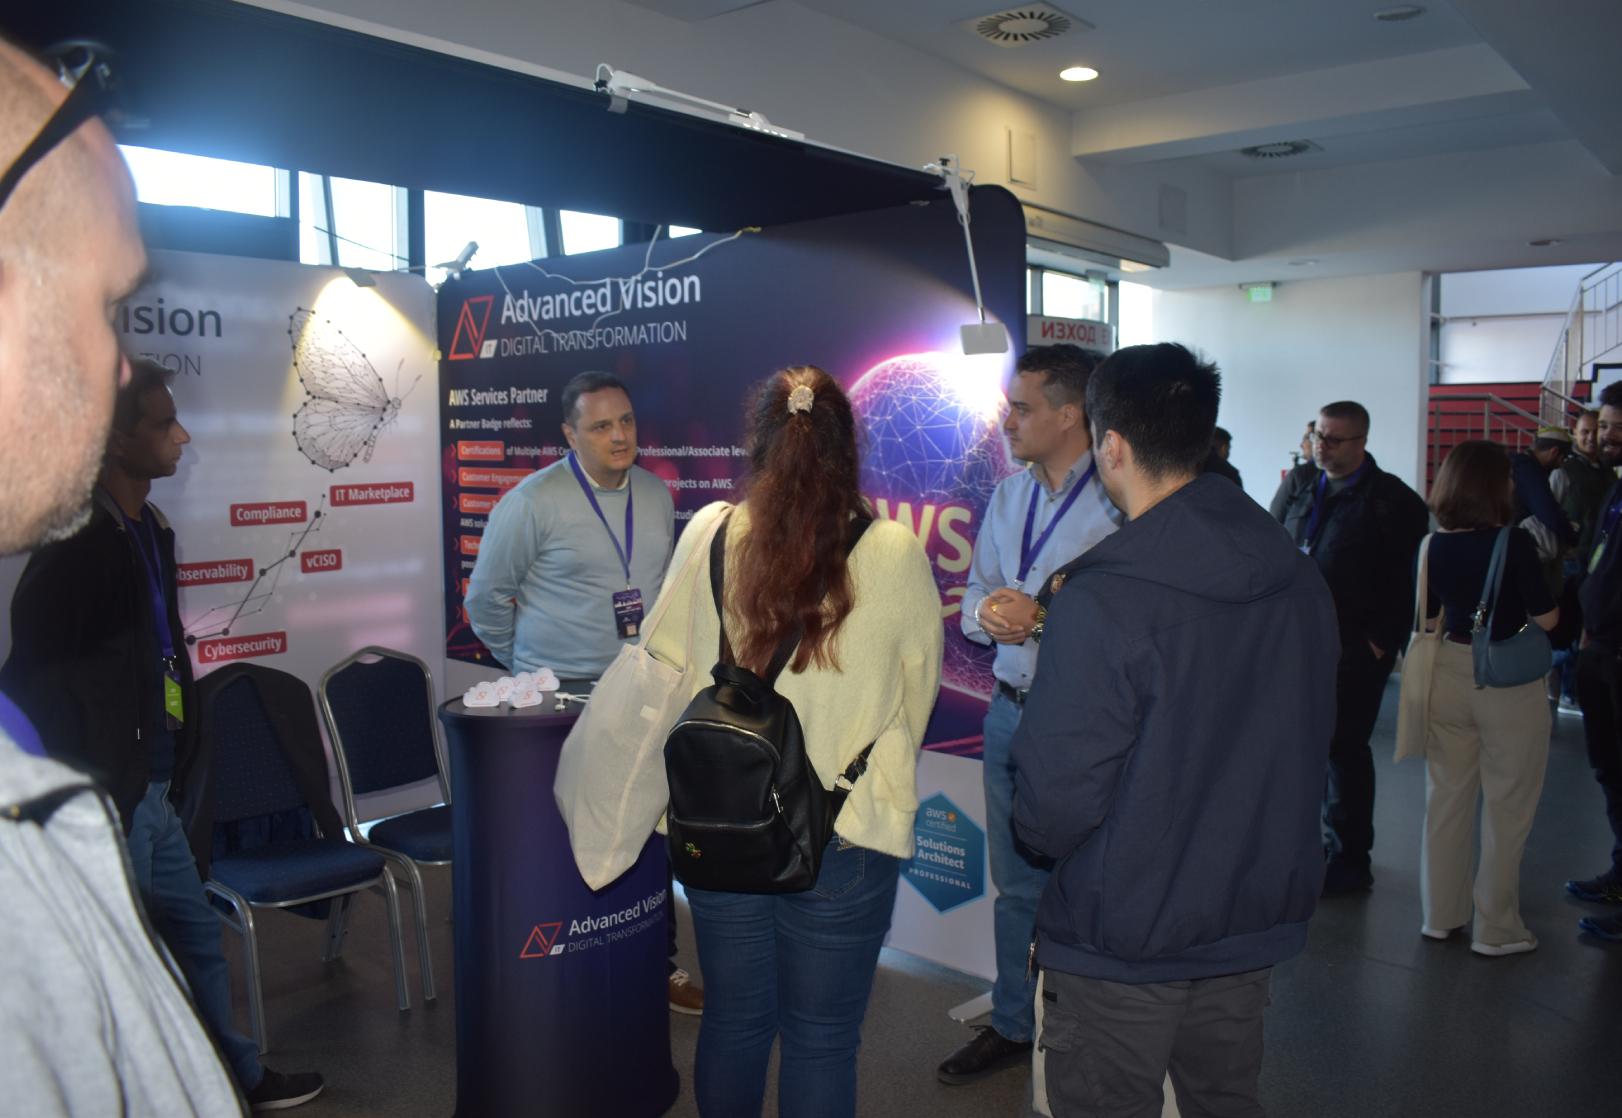
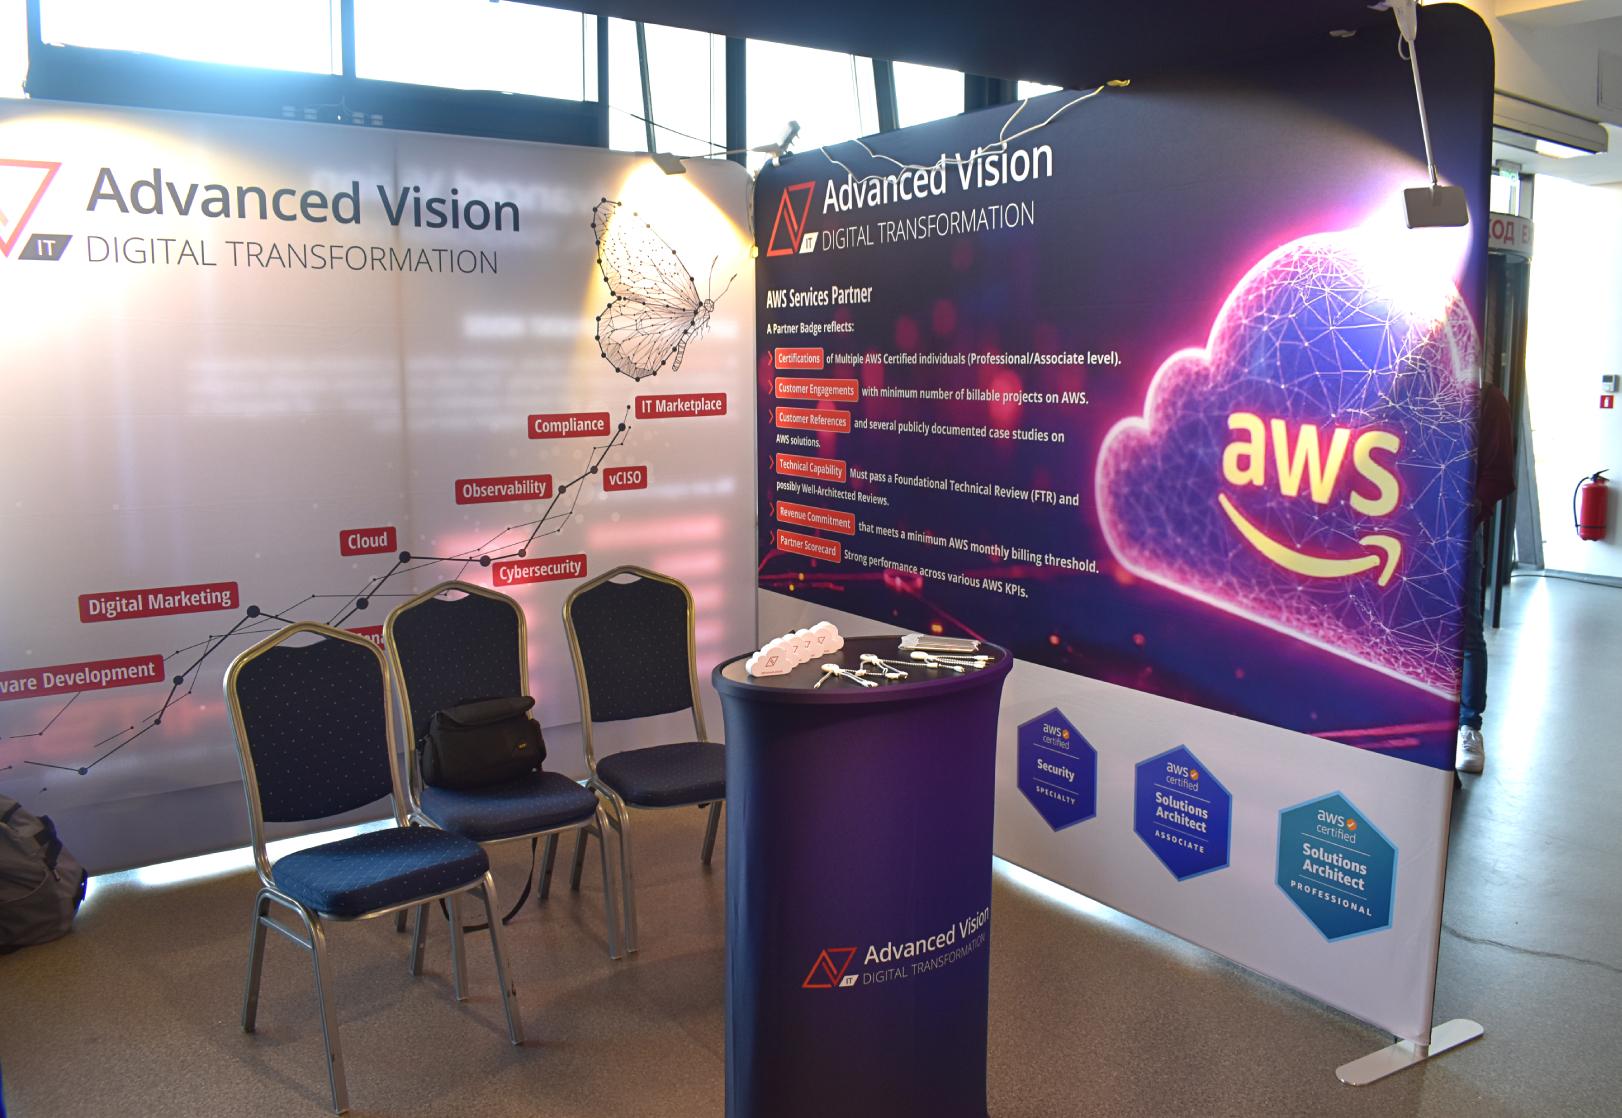
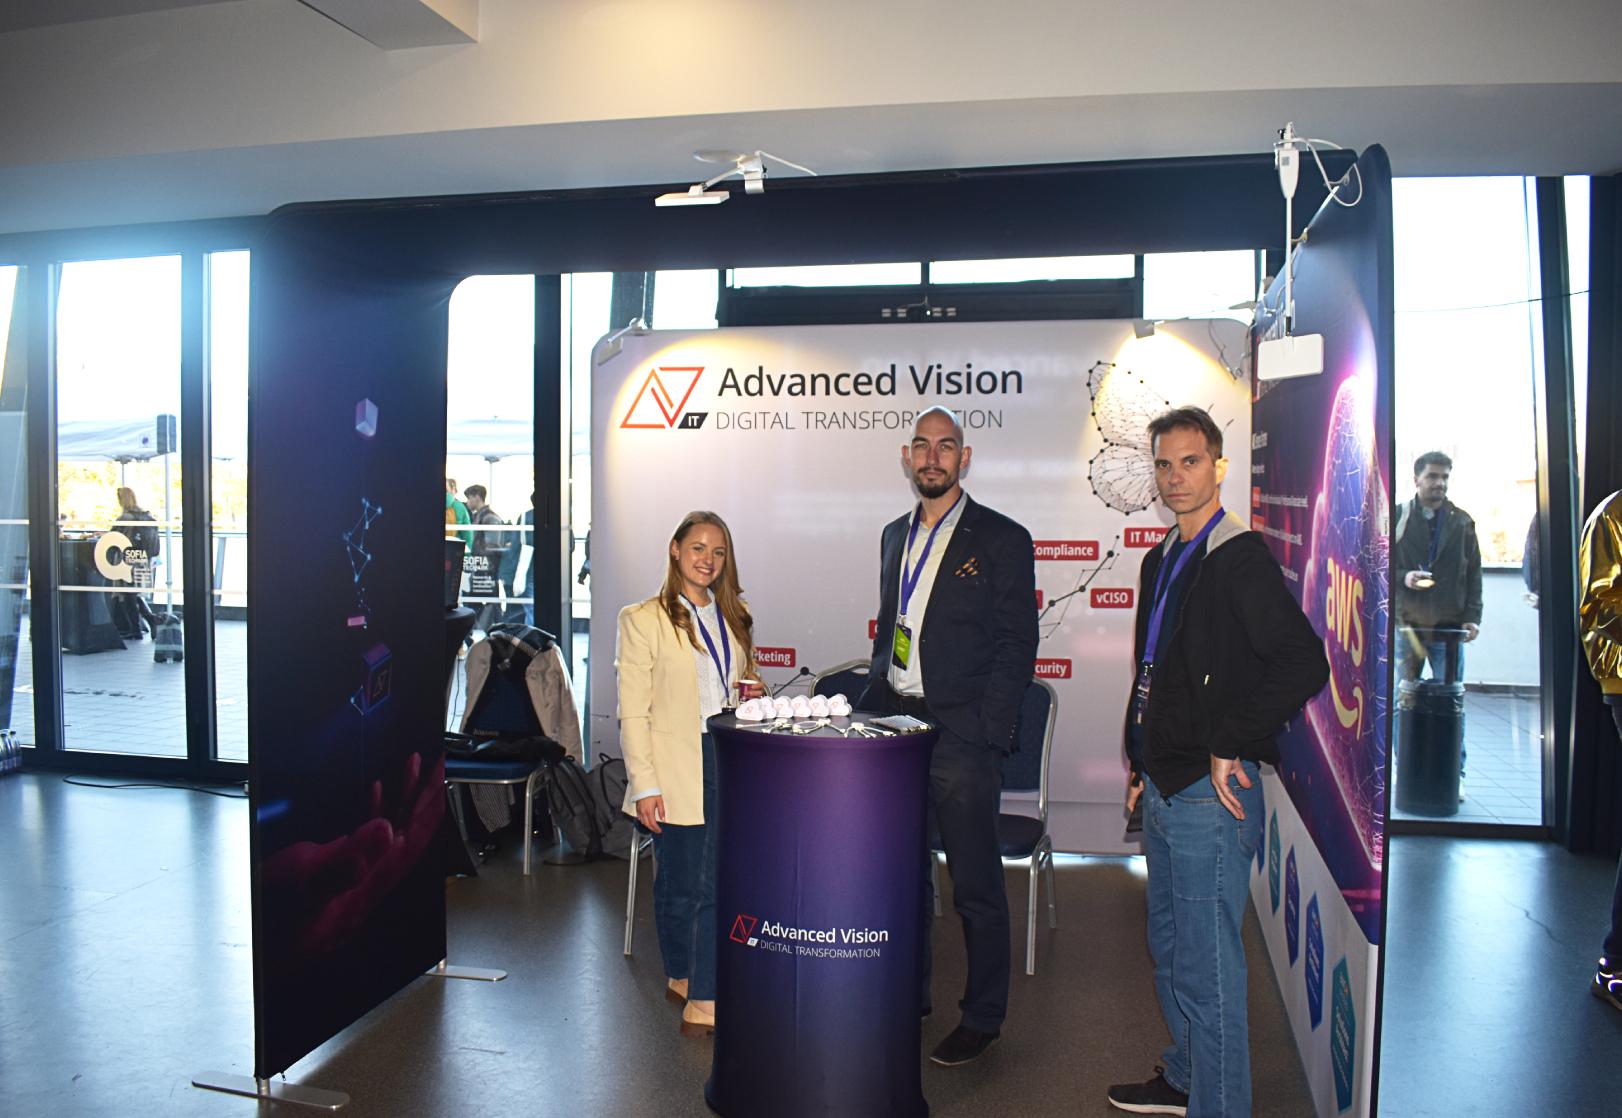
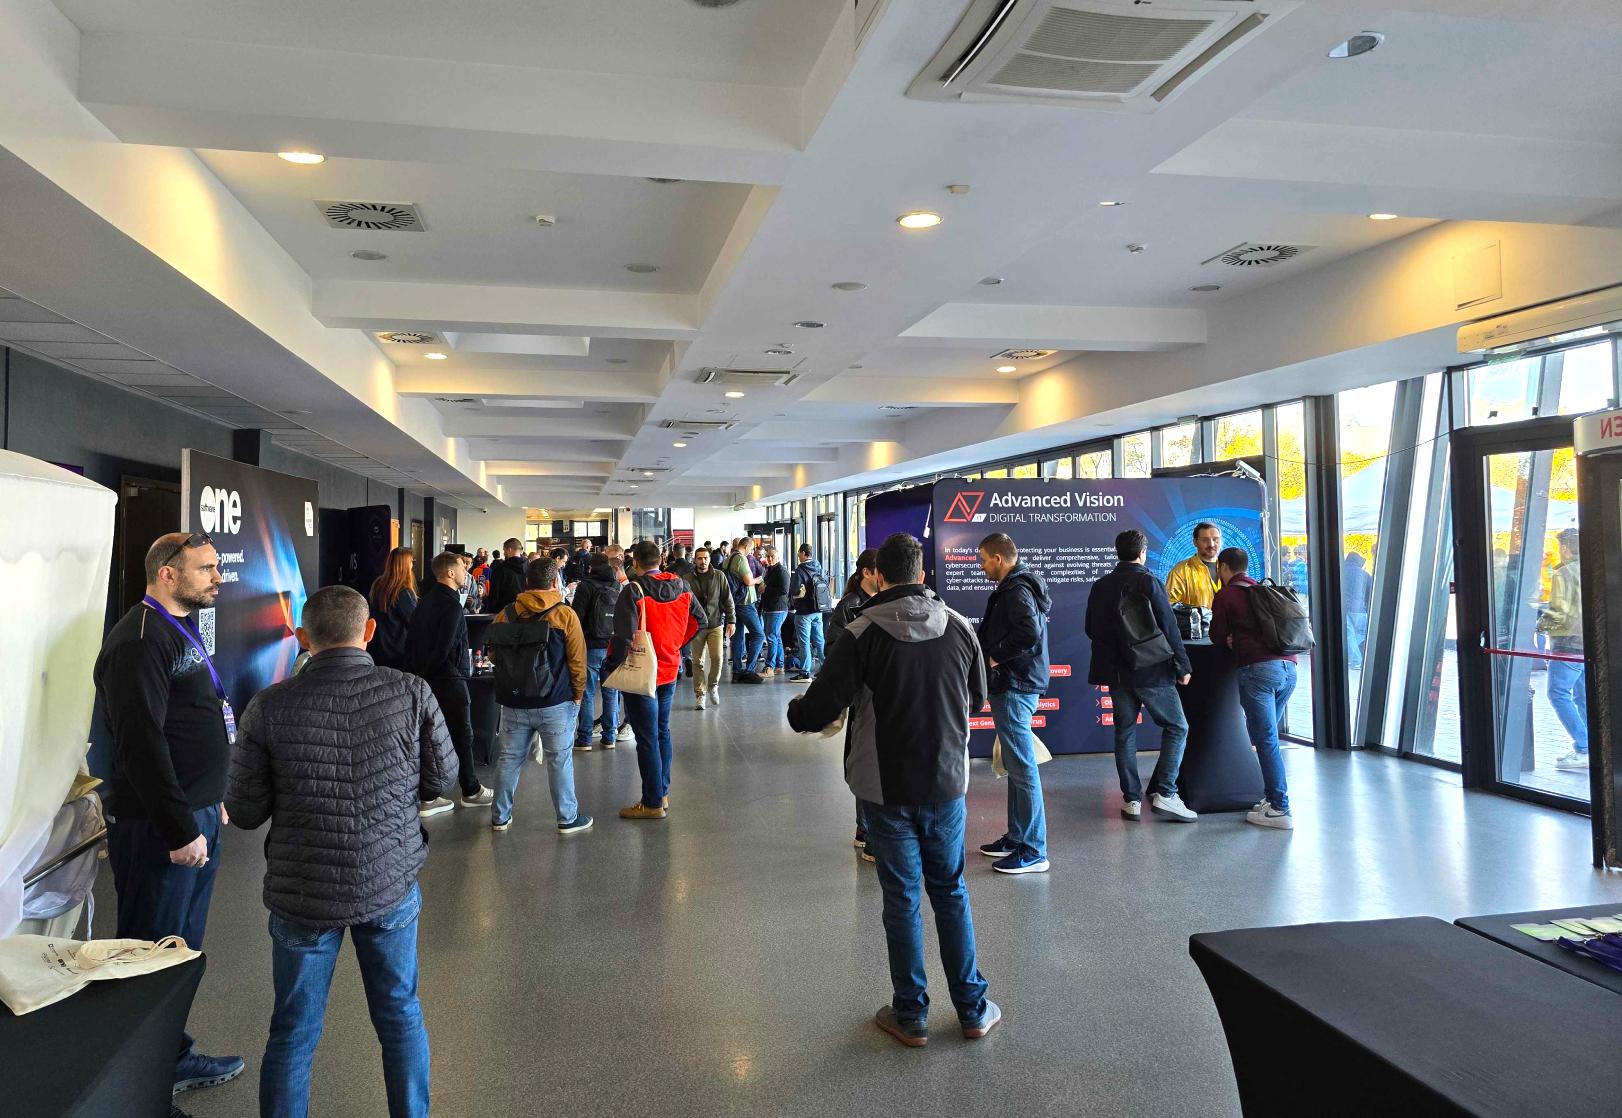
We believe that strong cyber resilience is built through knowledge, hands-on experience and active participation in the professional community. We engage in industry conferences, training programmes, technology vendor events, expert podcasts and initiatives focused on improving organisational cyber resilience.
In addition to helping organisations manage risk and strengthen their security posture, we actively invest in learning, knowledge sharing and the development of the professional community. This enables us to stay aligned with emerging technologies, evolving threats and industry best practices.
Active Participation in the Digital and Cybersecurity Ecosystem
We believe that cyber resilience and successful digital transformation are built through knowledge sharing, professional collaboration and active participation in the technology community. We support initiatives and organisations that contribute to the advancement of cybersecurity, innovation and business development.
Bulgarian Cybersecurity Association
We actively contribute to the development of cybersecurity in Bulgaria through participation in professional initiatives, expert discussions and knowledge-sharing activities.
Learn More →BAIT
Part of a professional network bringing together leading technology companies dedicated to advancing Bulgaria's ICT sector and digital economy.
Learn More →Digital Innovation Hub Trakia
Supporting initiatives focused on digital transformation, innovation, cybersecurity and improving the competitiveness of businesses across multiple sectors.
Learn More →ICT Cluster Varna
Supporting the development of the regional technology ecosystem through collaboration between businesses, innovation organisations and the ICT community.
Learn More →Bulgarian Industrial Association
Supporting sustainable and competitive business development through active participation in initiatives related to digital transformation, innovation, risk management and industrial growth.
Learn More →Our engagement with professional communities enables us to stay aligned with emerging technologies, regulatory requirements, evolving threats and industry best practices. We bring that knowledge directly to the organisations we support, helping them build more secure, resilient and competitive digital businesses.


CISO as a Service + SECaaS Packages
We combine strategic cybersecurity leadership with managed security services and protection technologies, enabling organisations to benefit from both expert guidance and practical mechanisms for reducing cyber risk.
Many organisations have technology without strategy, or strategy without effective protection. Our model combines risk management, strategic leadership and practical cybersecurity protection into a single service.
SOHO Protect
Ideal for:
1-10 employees
Includes:
→ Baseline Security Assessment
→ Security Policies & Procedures Pack
→ Vulnerability Management
→ Endpoint EDR Protection
→ Annual Security Review
Business Secure
Ideal for:
10-50 employees
Includes:
→ Comprehensive Security Assessment
→ Monthly Virtual CISO Session
→ Incident Response Plan
→ GDPR Readiness Checklist
→ Vulnerability Management
→ EDR Protection
Business Plus
Ideal for:
50-100 employees
Includes:
→ Continuous Monitoring
→ Compliance Roadmap
→ Quarterly Executive Reporting
→ Security Awareness Training
→ Vulnerability Management
→ EDR Protection
Executive Programme
Ideal for:
Organisations with 100+ employees
Includes:
→ Tailored Governance Programme
→ SOC Integration
→ Cloud Security Management
→ Executive Reporting
→ Fractional CISO Leadership
→ Custom Security Stack
Ready to Turn
Cyber Risk into a Business Advantage?
Gain clarity on your current cybersecurity posture, identify your most critical risks and build a practical roadmap with the support of experienced cybersecurity, cloud and risk management professionals.
📅 Schedule a Consultation 📊 Start Your NIS2 Self‑AssessmentFocused on real business risk
Practical recommendations and next steps
ADVANCED VISION IT - MALTA
Address: Suite 8, Ta’ Mallia Buildings, Triq In‑Negozju, Zone 3, Central Business District, Birkirkara, CBD 3010, Malta
Registration number: C111282, VAT Number: MT31713827
Phone:+35679224404
Email: office@advisionit.com
ADVANCED VISION IT - BULGARIA
Advanced Vision IT LTD
Address: District Triaditsa, Tulcha Street No. 46, Floor 6, Sofia, Bulgaria
ID No: 205789039,
VAT No: BG205789039
Phone: +359 888258530
Email: office@advisionit.com